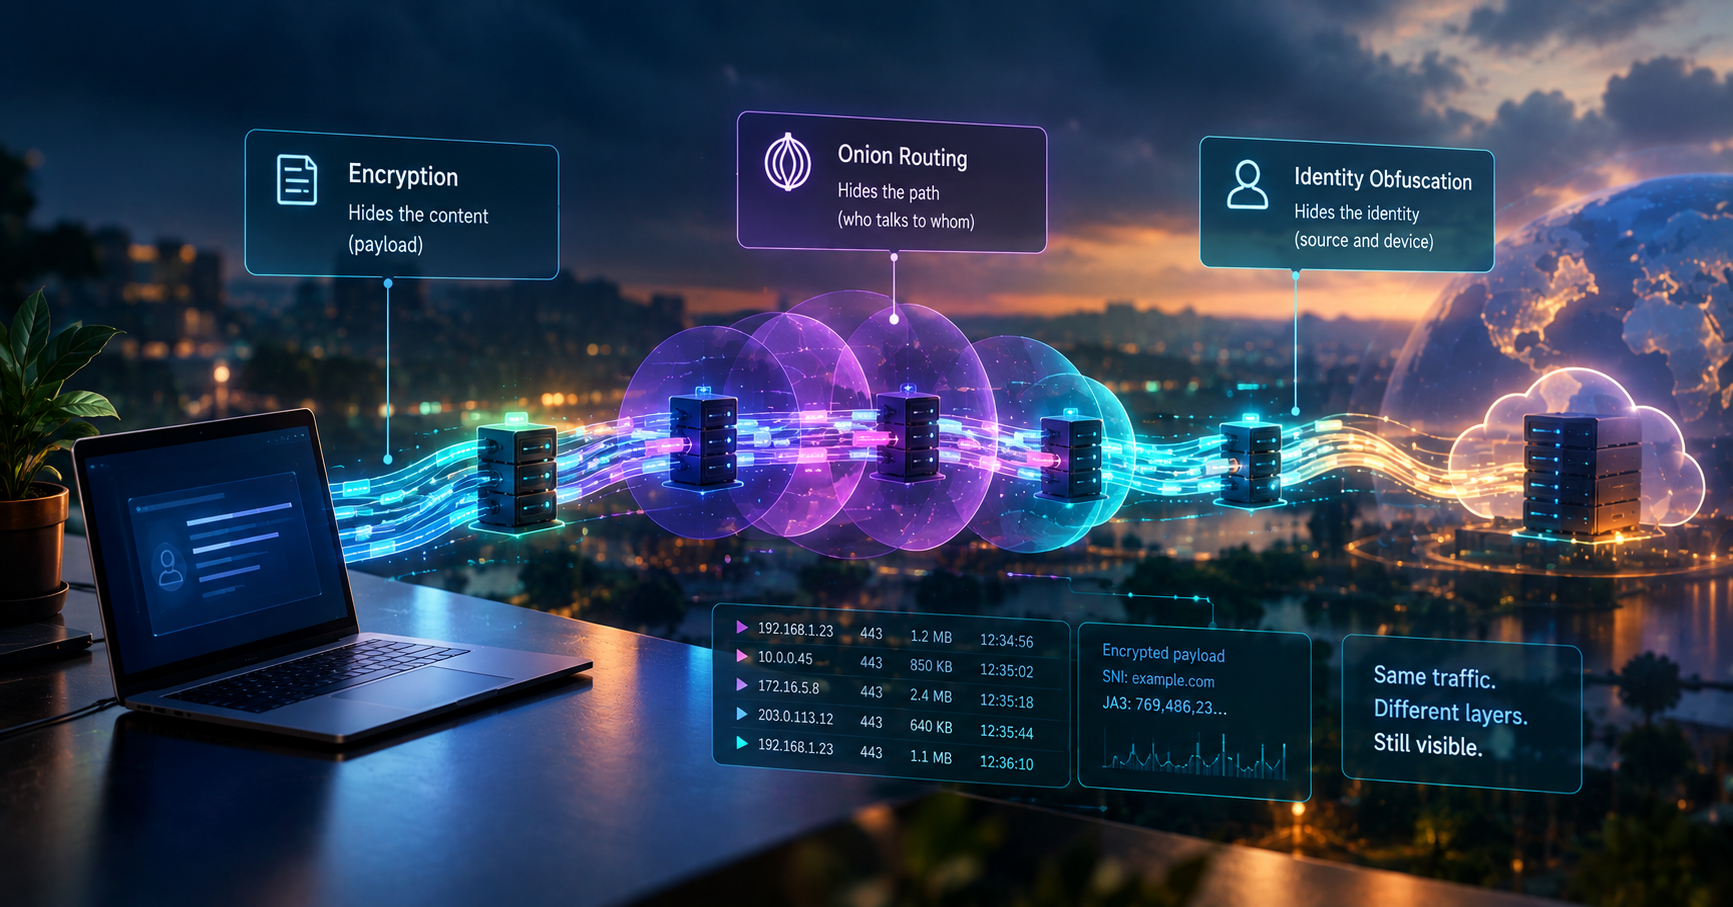
Hiding Network Connections: Encryption, Onion Routing, and Identity Spoofing
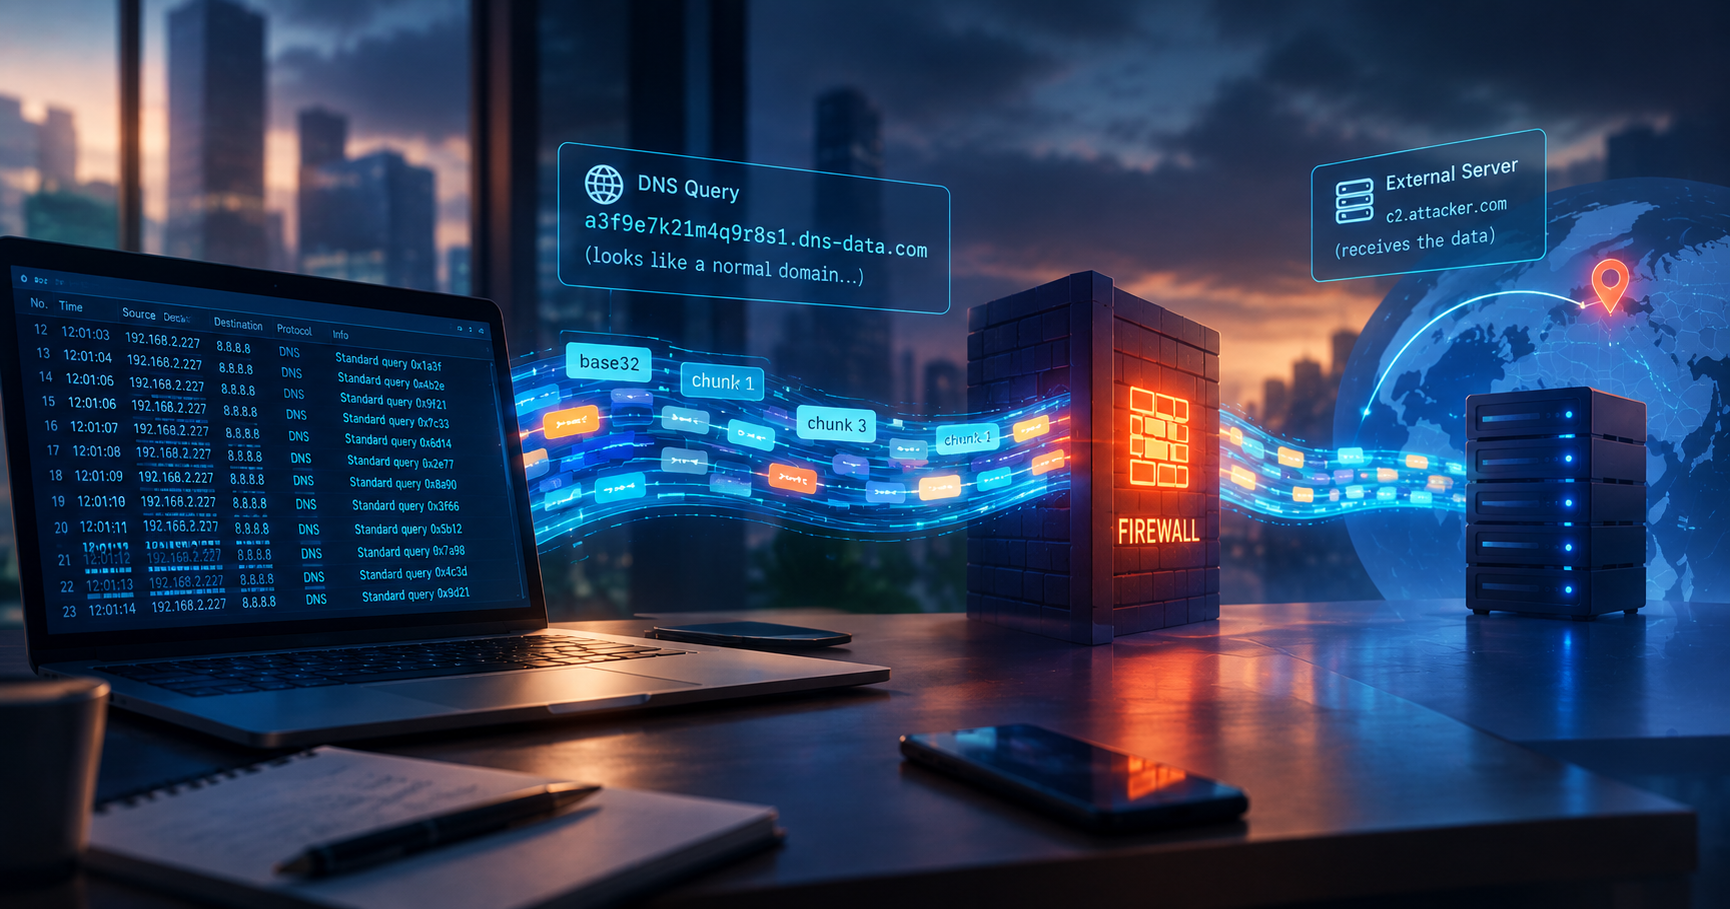
The content is encrypted, the path is anonymised, the origin is spoofed: but the connection is still visible
Sep 22, 202615 min read
Search for a command to run...
Series
Where Data Hides is a four-part series on data hiding and recovery across Windows, GNU/Linux, and the network layer. Each piece works from the artifact outward, an actual byte offset, command output, or packet capture, rather than describing a technique in the abstract, and pairs every hiding method with the exact way it gets found. The series closes with a NIST-based investigation walked through a case end to end, tying the file-system and network material back to how an examiner actually works a scenario in practice.
The content is encrypted, the path is anonymised, the origin is spoofed: but the connection is still visible
From IP headers to DNS queries: how covert channels work and how their traffic patterns give them away
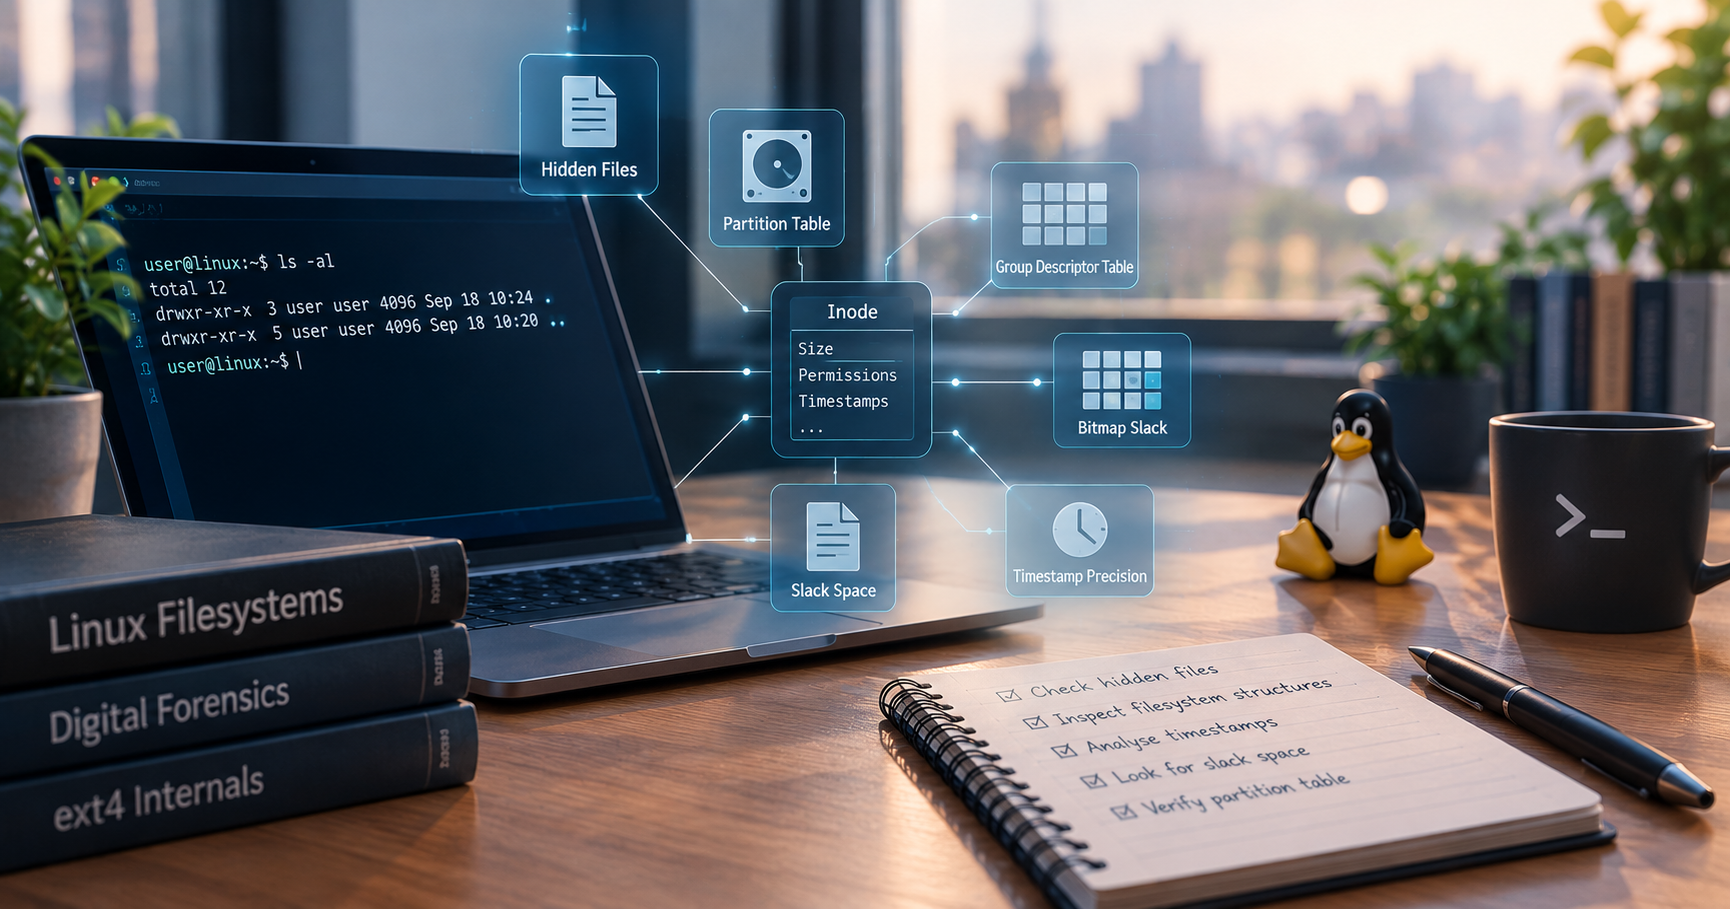
A partition table entry reading "Hidden FAT16." An inode field nobody writes to. A nanosecond timestamp carrying encoded data. Where GNU/Linux hides evidence and how investigators find it.
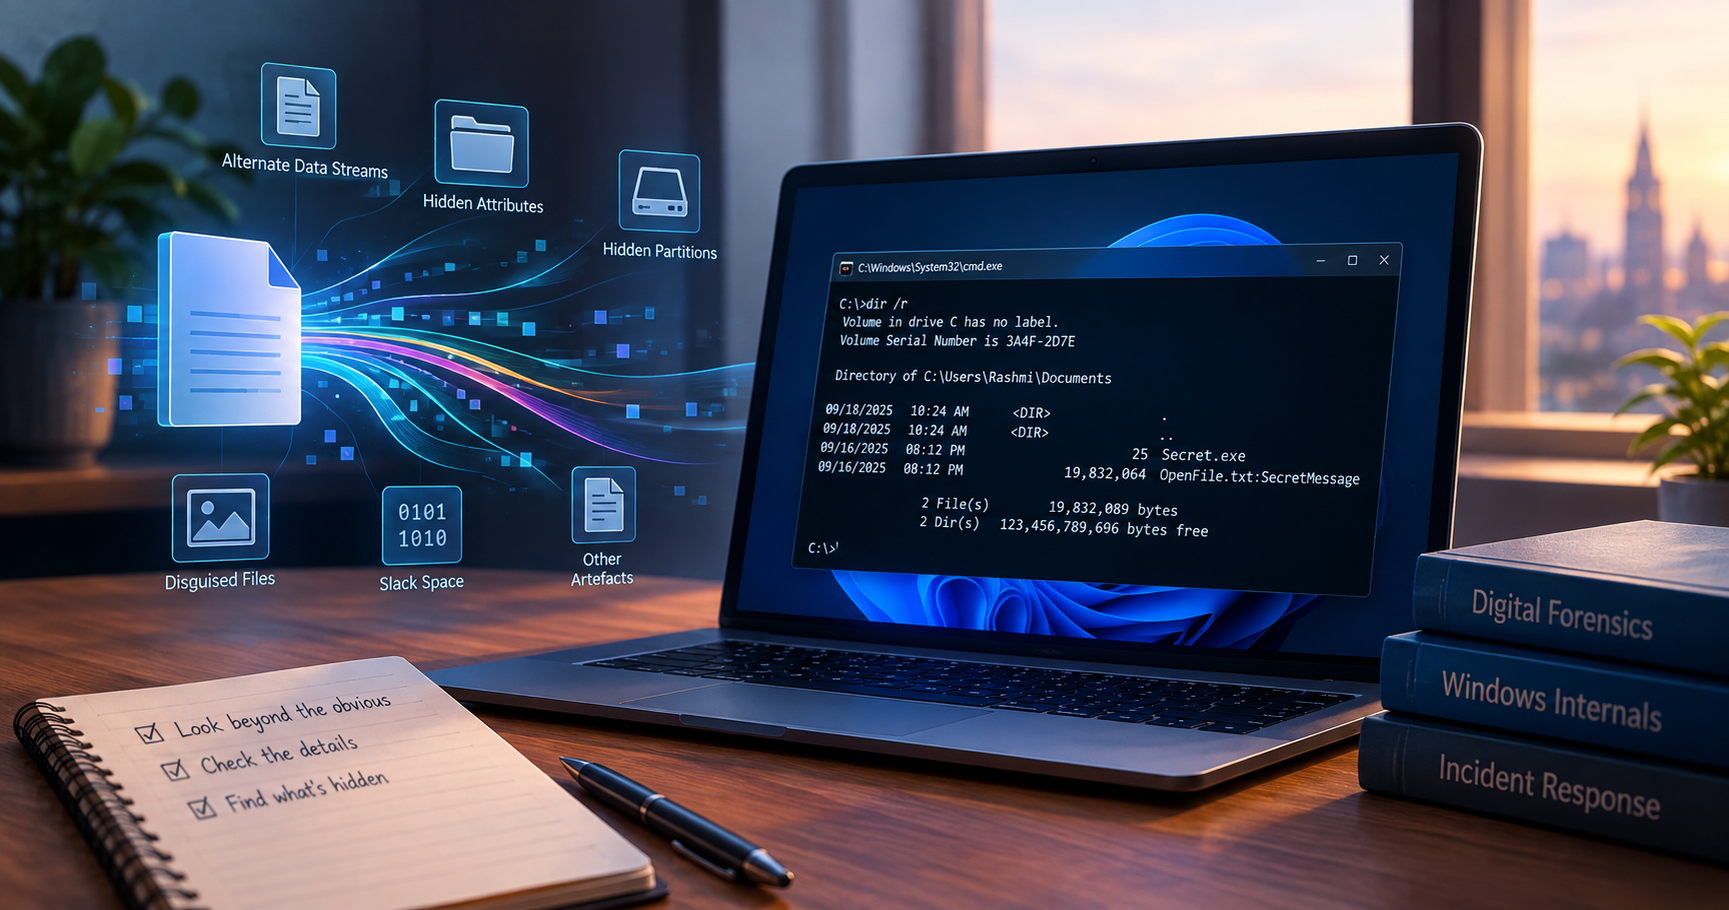
A file reports 25 bytes. A different command reveals 19MB attached to it. Where NTFS actually hides data, and the exact commands that find it.